The Node.js/PHP CVE and Bubble’s Reply: ‘No Claimed Customer-Data Access’ Is a Platform Note, Not Permission to Skip Your Plugins
Bubble said "No action is required from Bubble users." For an MVP builder, that's only half the story. The platform runtime is patched. Your plugins, API keys, and Privacy Rules are still yours to check.
A Node.js or PHP vulnerability makes the headlines, and founders and vibe-coders building their first minimum viable product (MVP) with nocode tools come to me with two questions. Is my startup's database exposed? Should I be fixing something on the server from inside the visual editor?
My answer: first separate what the hosting platform is responsible for from what you are responsible for. Once you do that, the panic goes away and the real checklist becomes obvious. Same topic: Bubble MCP: A First-Connection Checklist.
What Bubble Confirmed at the Platform Level
After the security advisories on Node.js and PHP, Bubble published an incident note. Here is what its self-assessment says:
- Parts of Bubble's infrastructure run on Node.js, and Bubble deployed the relevant security updates and patches there. Bubble does not run PHP.
- Bubble found "no way to use these vulnerabilities to access customer data or gain elevated privileges."
- The platform saw "no sign of exploitation since the disclosure."
- The takeaway for app creators: "No action is required from Bubble users." Their engineering team keeps monitoring.
What This Means for Fast MVP Builders and Vibe-Coders
If you're moving fast to validate a market hypothesis, collect user feedback, or pitch early-stage investors, keep one boundary in mind: you cannot and should not try to patch infrastructure inside the Bubble editor. Same topic: n8n 2.35+: Agents preview, MCP,.
Bubble is a fully managed hosted runtime. Bubble's team handles low-level dependencies, Node.js runtime patching, and core server configuration. Building workflow workarounds against a low-level server CVE is unnecessary, and in a nocode environment it's impossible anyway.
But I read Bubble's statement on customer data literally. It's a platform-level assessment of their own runtime. It is not an automated security audit of how you configured your app.
The Shared Responsibility Model
Bubble's official documentation describes a shared security responsibility model between Bubble, AWS, and the app builder:
- Bubble and AWS maintain the underlying hardware, networking, server operating systems, and core hosted software.
- App Builders are solely responsible for database permissions, user access settings, secure handling of secrets, and external integrations.
A platform patch protects Bubble's infrastructure. It does nothing about exposed database tables, missing permissions, or leaked API secrets in your app. Same topic: Bubble Secrets Scanner: How to.
Third-Party Plugins Remain Your Responsibility
This matters most when you assemble an MVP from marketplace add-ons. Bubble's Vulnerability Disclosure Policy says outright that "3rd-party plugins not developed by Bubble" are out of scope.
When you pull community plugins in to test features quickly:
- A platform statement about Node.js patching is not an audit of third-party marketplace code.
- Community plugins can talk to external private backends or APIs with their own unvetted vulnerabilities.
- Bubble's clean infrastructure report doesn't let you skip plugin hygiene.
A Practical MVP Security Checklist Before Launch
You don't need deep technical skills or weeks of compliance prep to validate an MVP safely. Before you onboard early users, I'd do this baseline:
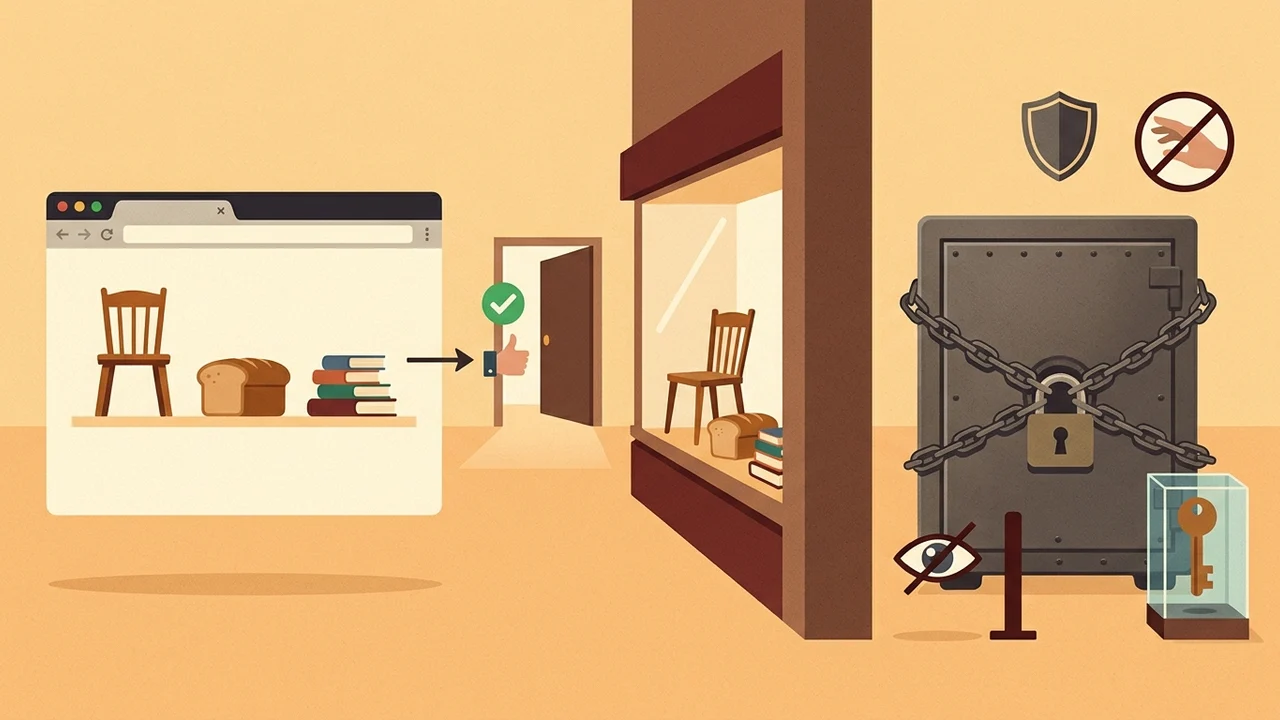
- Leave Hosting to the Platform: Bubble confirmed its runtime is patched and no builder action is required. Take that at face value and get back to your product.
- Implement Server-Side Privacy Rules: Bubble's documentation calls Privacy Rules "essential" for securing sensitive data. They enforce access on the server. Hiding elements or groups in the visual editor doesn't stop anyone from seeing the data over the network.
- Keep Third-Party Plugins Minimal: Install only the community plugins you strictly need to test your core value proposition. Remove the ones you don't use. Skip unverified extensions that ask for excessive permissions.
- Safeguard API Keys and AI Tokens: When you connect external APIs or AI workflows, mark secret keys in the API Connector as private (server-side only) so they never reach the client's browser.
| Checklist item | What it is for | What it is not for |
|---|---|---|
| Leave hosting to the platform | Trust Bubble’s patched runtime and focus on your product; no builder action required | Taking on platform patching or runtime security yourself |
| Implement server-side Privacy Rules | Enforce sensitive-data access on the server (Bubble docs call them “essential”) | Relying on hiding elements or groups in the visual editor (data can still be seen over the network) |
| Keep third-party plugins minimal | Install only community plugins you strictly need to test your core value proposition; remove unused ones | Keeping unverified extensions that ask for excessive permissions |
| Safeguard API keys and AI tokens | Mark secret keys private in the API Connector (server-side only) when connecting external APIs or AI workflows | Exposing secrets to the client’s browser |
Speed is the main advantage of nocode when you test new ideas. But a resilient platform only guarantees the foundation. The data inside your MVP is still yours to protect.