Cursor Rollouts and Security Review: Guarding Deploys in Nocode and Vibecoding MVPs
Cursor announced Rollouts for post-deploy monitoring and Security Review for PR vulnerability checks. I go through how non-technical founders can use them to ship fast without breaking prod.
Picture a founder building an MVP on a nocode platform like Bubble and using Cursor to vibecode the backend logic or APIs. The hard part is the last mile. Changes have to reach production without breaking existing user flows or opening a security hole. On September 23, 2026, Cursor released two bots for exactly this post-PR phase: Rollouts and Security Review. A closer look: Expo SDK 57 in Bubble. Same topic: BuildGate: approve live deploys before.
If you're a non-technical founder validating an idea, collecting user feedback, or pitching early investors, these give you a practical safety net against regressions. A closer look: Salesforce Builder Central Beta: Why.
How Cursor Rollouts Works
Before deployment, Rollouts posts a monitoring plan in your PR comments. The plan lists the risks it found, the expected blast radius, the key metrics to watch, and any missing instrumentation.
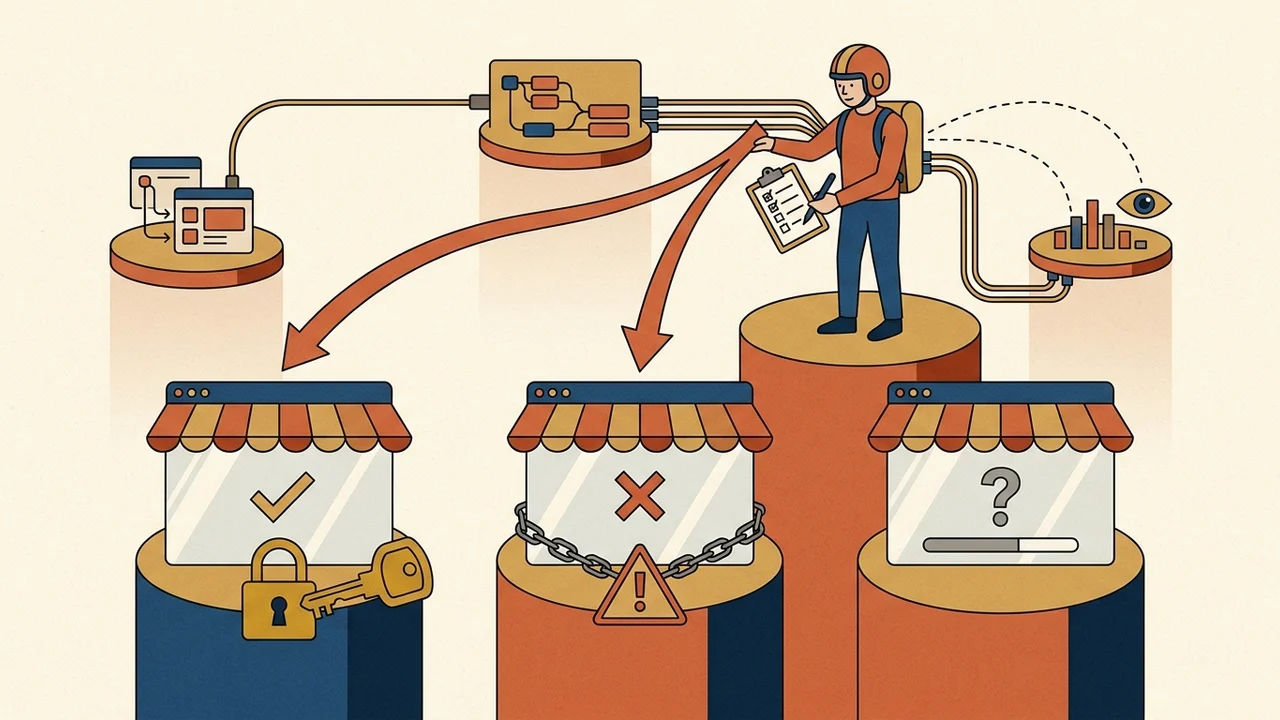
- Tracking live rollouts: The bot listens to deployment events from your CD pipeline and checks health for each environment separately. Each release gets one of three tags: verified healthy, regression detected, or inconclusive.
- Integrations: It works with GitHub or Origin, CD systems, and observability platforms. Datadog is officially supported, and Cursor's blog also highlights Grafana and Honeycomb.
- Handling regressions: When it detects a problem, Rollouts alerts the author. Depending on your team settings, it can open a revert PR for a human to review, or pass the issue to a cloud agent to prepare a fix. It won't merge or roll back on its own without someone signing off.
Security Review: Catching Exploitable Flaws
Bugbot handles code quality and formatting. Security Review (the product blog calls it Security Reviewer) only checks PRs for vulnerabilities someone could actually exploit, and it reads them in the context of the whole repository. It skips draft PRs automatically.
You get a single PR comment with all the findings: the exact attack path, the severity, and a proposed code fix. If a warning doesn't apply, you can dismiss it and say why, or set up custom team rules.
Practical Takeaways for Early-Stage Builders
- Plan requirements: Both features are only on Cursor Teams and Enterprise plans. You turn them on in the automations tab of the dashboard.
- Rollouts promo credits: Cursor offered usage credits for the "next 10 days" after the September 23, 2026 launch (~50 changes on Teams, ~500 on Enterprise). That window ends around October 3, 2026.
- Instrumentation matters: If your project has no proper metrics or error logs, Rollouts will come back inconclusive. If you're pairing Bubble with custom code, turn on baseline logging before you start relying on automated deploy checks. Worth reading next: Bubble, Reverse.dev for Teams, and. Worth reading next: Bubble Business of Building 2026:.